ARM Template Refactoring: Understanding the Impact Before Deployment
Infrastructure as Code has become the foundation of modern Azure deployments. ARM templates allow organizations to deploy environments consistently, automate provisioning, enforce standards, and scale cloud operations with confidence.
But ARM templates rarely remain static.
Applications evolve. Security requirements change. New Azure capabilities emerge. Naming standards are updated. Technical debt accumulates.
Eventually, every ARM template must be modified.
The challenge is that some seemingly simple changes can have far-reaching consequences. A parameter rename, API version update, or dependency modification may appear harmless, yet those changes can unexpectedly affect deployments, automation, and production workloads.
The danger is not the change itself. The danger is the hidden impact of the change.
This is the problem Safe Update Governance in Maestro Studio ENSEMBLE is designed to solve.
Rather than showing developers only what changed, ENSEMBLE helps them understand what those changes may affect before deployment.
For example, a user changes the Location parameter name to 'locationA':
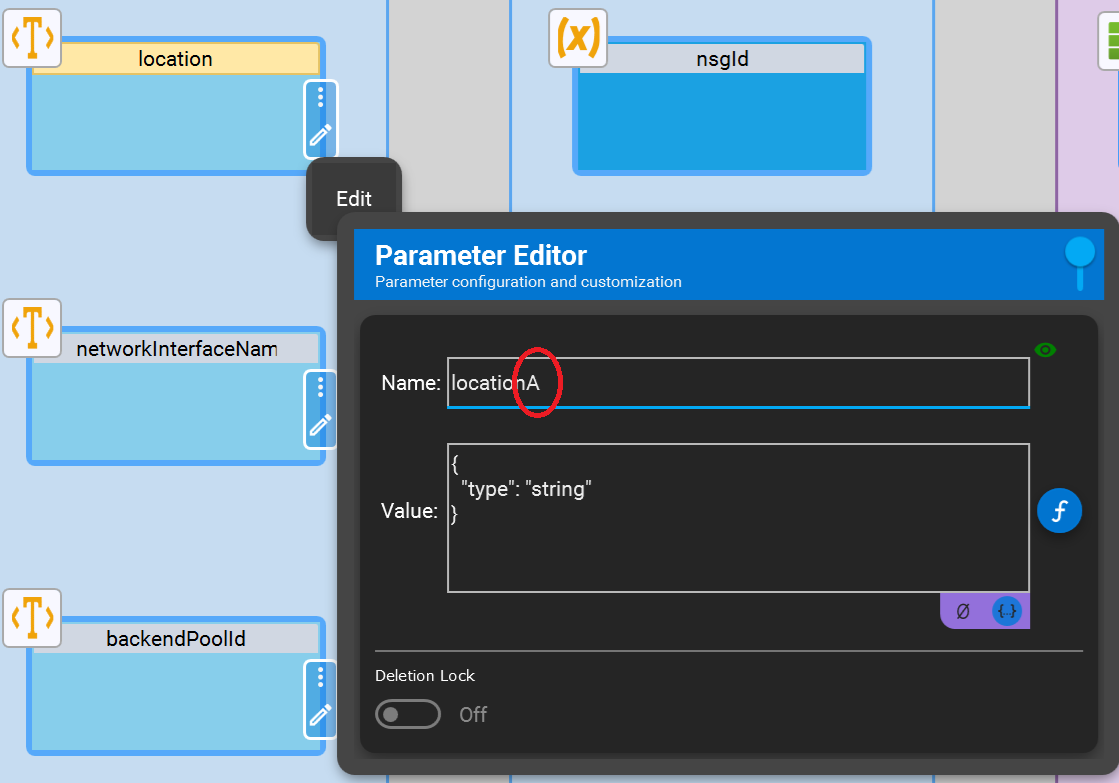
Image 1. Location Parameter Name Change example.
As soon as the change is introduced, ENSEMBLE automatically validates the entire template, including hidden expressions/functions, and alerts the user of the issues created due to the recent parameter name change, see screenshot below, Image 2. ENSEMBLE displays multiple warning icons throughout the Visual Canvas; and when the user clicks on the warning sign located on the impacted area, ENSEMBLE displays the detailed warning message:
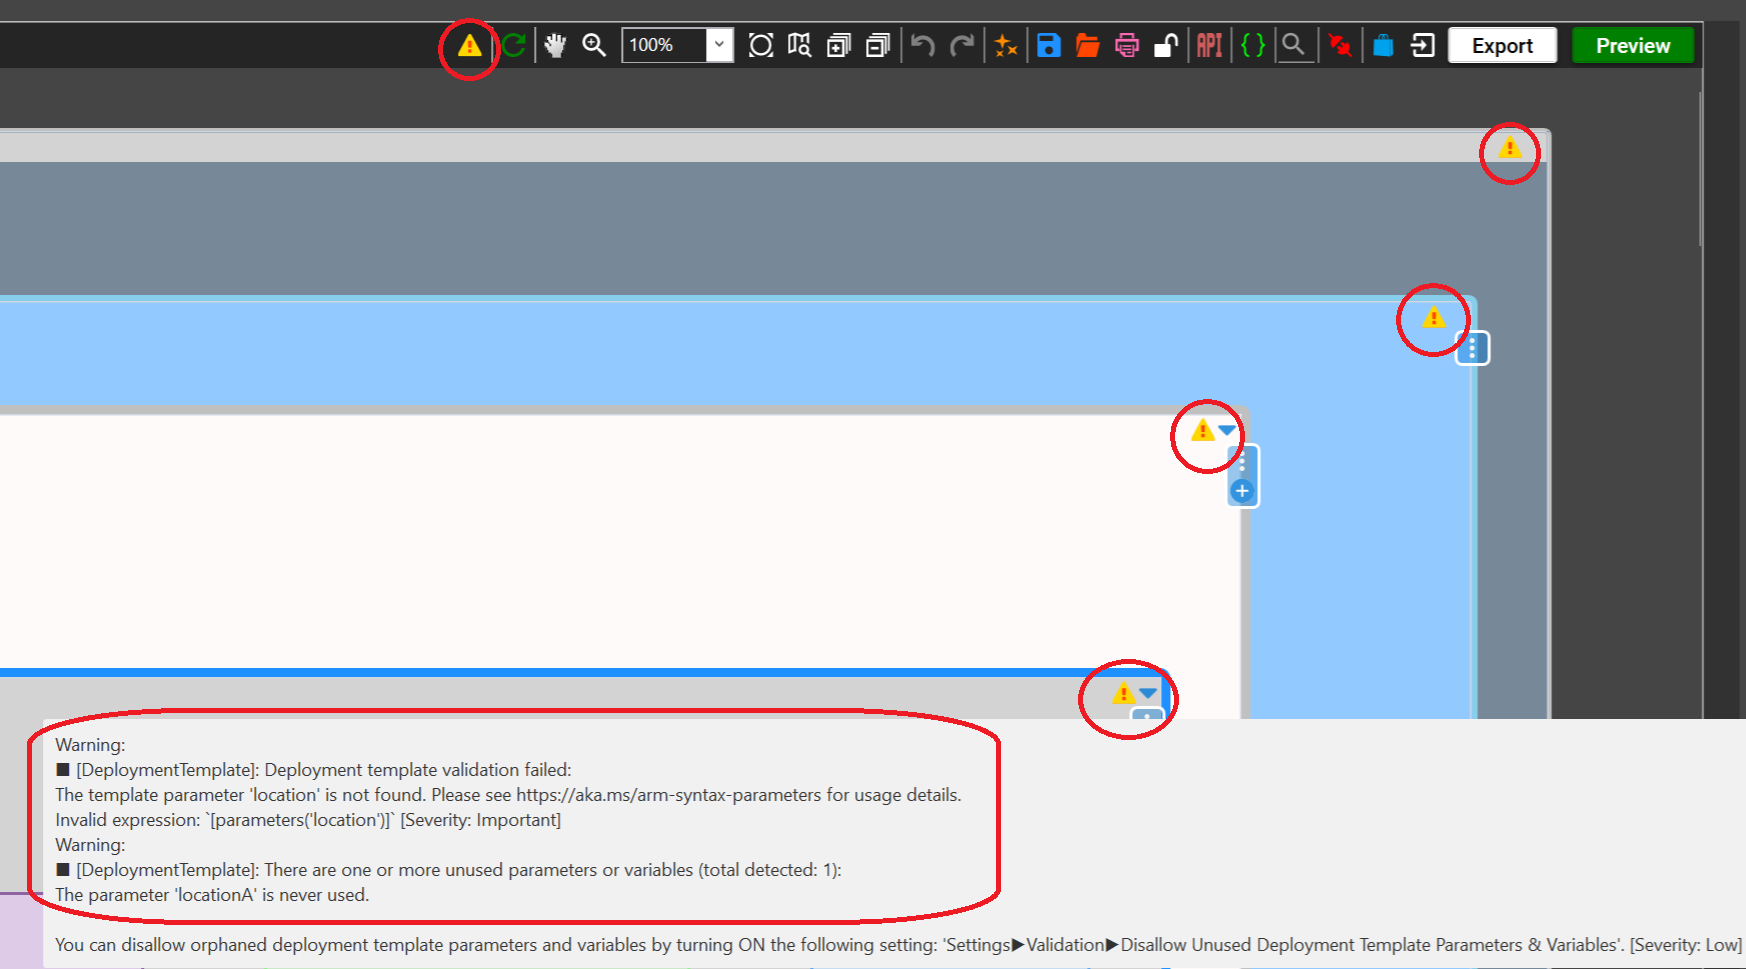
Image 2. Safe Update Governance by ENSEMBLE, in action.
The user has the option to remove the update that triggered the warning signs or update the affected expressions to use the newly renamed location parameter.
Why ARM Refactoring Is Different
As ARM templates grow, they become increasingly interconnected.
Developers routinely:
- Rename parameters
- Update API versions
- Reorganize resources
- Simplify expressions
- Standardize naming conventions
These changes improve maintainability, but they can also affect:
- Resource configurations
- Hidden expressions
- Deployment outputs
- Dependency relationships
- CI/CD pipelines
- Automation and integrations
A small edit in one area of a template can ripple throughout the deployment model.
Traditional Diff Tools vs. Impact Analysis
Traditional comparison tools answer a simple question:
What changed?
That's great and useful but they don't answer the more important question:
What should I review because of this change?
That's where Safe Update Governance adds value:
- Saves time
- Money
- Frustration
- And troubleshooting headaches
Rather than treating an ARM template as a collection of JSON sections, ENSEMBLE analyzes relationships between parameters, variables, resources, expressions, outputs, and dependencies.
Common Refactoring Risks
Parameter Renames
A parameter rename is not simply a text change, as we saw in Images 1 and 2 above.
It may affect:
- Expressions
- Resource properties
- Conditions
- Outputs
- Nested deployments
An incomplete update can introduce validation failures, broken references, or unintended deployment behavior.
Safe Update Governance helps reveal those affected relationships before deployment.
API Version Updates
Updating an API version may require a review of:
- Added or removed properties
- Changed requirements
- New provider capabilities
- Modified behavior
While a traditional diff reports that the API version changed, ENSEMBLE highlights the need for compatibility review before deployment.
Expression Chains
ARM templates often contain indirect relationships.
A parameter may feed a variable, which then drives resource names, properties, conditions, and outputs.
As templates grow, tracing those chains manually becomes increasingly difficult.
ENSEMBLE analyzes these relationships and helps expose the downstream effects of a change.
Dependency Changes
Dependencies determine deployment ordering and parallelism.
Removing or modifying a dependency may not be dangerous, but it can affect how Resource Manager schedules deployment operations.
Safe Update Governance helps identify dependency changes and highlights areas that may require additional review.
Beyond Comparison: Understanding Impact
After identifying what changed, ENSEMBLE evaluates the impact of those changes through:
- Dependency analysis
- Expression analysis
- Output and interface review
- Validation checks
- Safe refactoring analysis
This helps developers identify risks that traditional text comparisons cannot easily reveal.
Examples include:
⚠ Hidden expression affected
⚠ Dependency chain modified
⚠ Output interface changed
⚠ Deployment behavior may require review
Protecting Automation
Many organizations rely on ARM template outputs to drive automation.
A template may deploy successfully while a pipeline, script, or integration fails because an output changed unexpectedly.
Safe Update Governance helps surface these downstream impacts during design and review instead of after deployment.
Refactor with Confidence
Successful Azure teams need more than version comparison.
They need visibility into:
- Hidden dependencies
- Expression relationships
- Deployment sequencing
- Output interfaces
- Potential breaking changes
That is the purpose of Safe Update Governance in Maestro Studio ENSEMBLE.
Conclusion
Every ARM template eventually changes.
The challenge is not making the change.
The challenge is understanding everything that changes touch, before deployment begins.
Traditional comparison tools answer:
What changed?
ENSEMBLE's Safe Update Governance goes further by helping developers understand: What will this change affect?
Knowing what changed is useful.
Knowing what that change will affect is essential.
To learn more about Maestro Studio ENSEMBLE, visit us on the Microsoft Marketplace: Maestro Studio ENSEMBLE | Microsoft Marketplace